

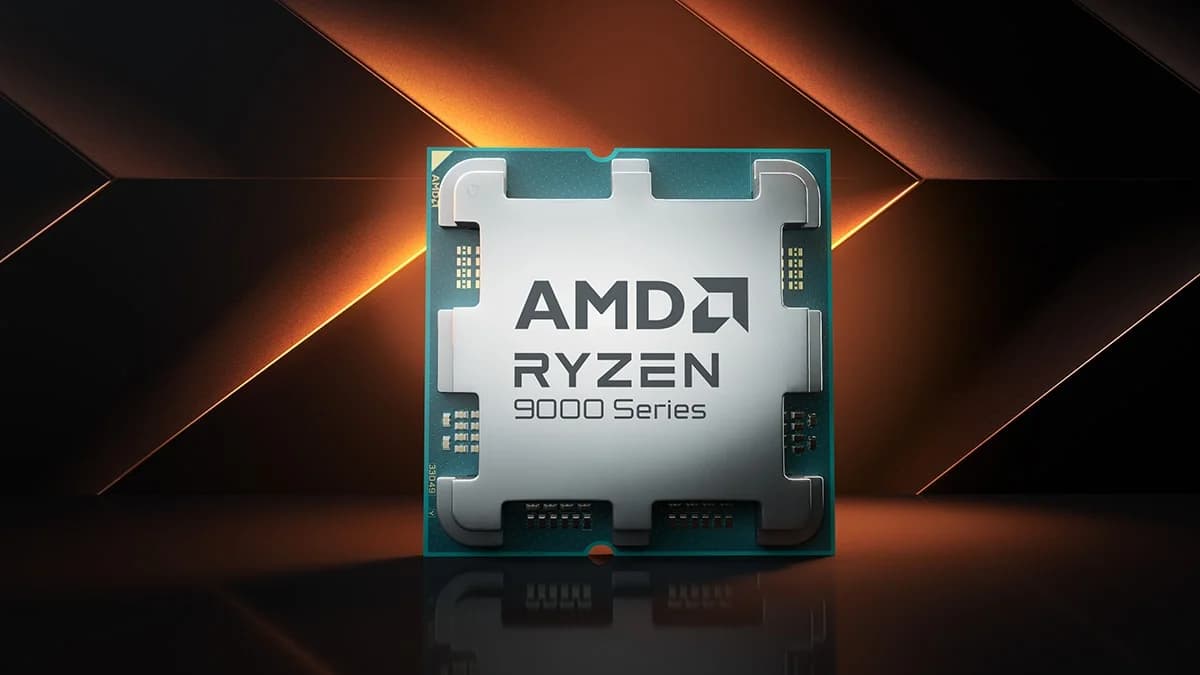
AMD confirmed two serious TPM 2.0 vulnerabilities on August 14, covering practically the entire current Ryzen lineup: everything from Ryzen 3000 through the latest Ryzen 9000, plus Ryzen AI 300 and 400, Ryzen AI Max 300, Threadripper, and the Ryzen Z1 and Z2 chips used in handheld consoles. If you're gaming on an AMD-based PC built any time in the last six years, this likely applies to you too.
What's actually broken
CVE-2026-6726 rates 8.5 on the CVSS 4.0 scale, "High" severity. The root cause is an error in how the TPM reference code separates different object types: a use-after-free condition lets information from a previously used TPM object stay resident in memory even after that same memory region gets reused for something else. In practice, that could let an attacker recover credentials from a TPM-aware certificate authority, and from there potentially falsify TPM encryption keys or other hardware attestation mechanisms.
CVE-2026-6727 is a timing side-channel vulnerability affecting RSA decryption workloads, rated 8.3 on CVSS. The flaw could theoretically let an attacker decrypt encrypted data or forge TPM 2.0 attestation keys by measuring tiny differences in how long cryptographic operations take to complete.
Why this is less scary than it reads on paper
Both vulnerabilities require local, privileged access, they can't be exploited remotely just by being connected to the internet. That's an important limit: to actually use either flaw, an attacker would already need administrative access to your machine, which is a serious security problem on its own, independent of TPM. For the average gamer or home user, the practical risk of a real attack is low, as long as nobody untrusted has physical or remote admin access to the machine.
The risk goes up in environments where multiple users share the same hardware, corporate workstations, cloud virtual machines, or public terminals, where one user with limited privileges could theoretically target another user's data on the same machine through the TPM layer.
What TPM actually does
TPM, Trusted Platform Module, is a dedicated, secure area in the processor or on the motherboard responsible for storing encryption keys and verifying system integrity before Windows even fully boots. It's the exact same module Microsoft made a mandatory requirement for installing Windows 11, and the thing behind features like BitLocker full-disk encryption and Windows Hello. AMD implements TPM as fTPM, meaning it lives in the processor's firmware rather than as a separate physical chip on the motherboard, a cheaper and more common approach in most modern PCs, but it also means a flaw in this implementation hits every processor of a given generation at once, not one bad batch of chips.
Fixes already exist, they just need installing
AMD has been working with motherboard vendors on fixes since May 2026, so for most popular boards, BIOS updates have already been available for months, well before the company officially confirmed the flaws themselves. Asus, MSI, and Gigabyte have all confirmed their own fixes for their respective motherboard lines. The problem is that a BIOS update is exactly the kind of step most users skip until something forces their hand, and plenty of systems still running the factory BIOS from the day they were bought remain vulnerable even though the patch is sitting ready to download.
Checking whether your motherboard has an update available takes a few minutes: the manufacturer's site, the support section, your board model, the changelog on the latest BIOS. If the description mentions a TPM fix, AGESA, or a firmware security patch from the last few months, it's worth installing, even if the practical risk to a home user is small. A BIOS update isn't as trivial as a routine driver update, so it's worth doing once, deliberately, rather than leaving a system exposed to a flaw whose fix has been sitting ready for months.
Comments
Discussion
Join the conversation around this story.
Join the discussion
Sign in to comment and reply to other readers.
Sign inNo comments yet
Start the discussion first.